Introducing MCP Scanner
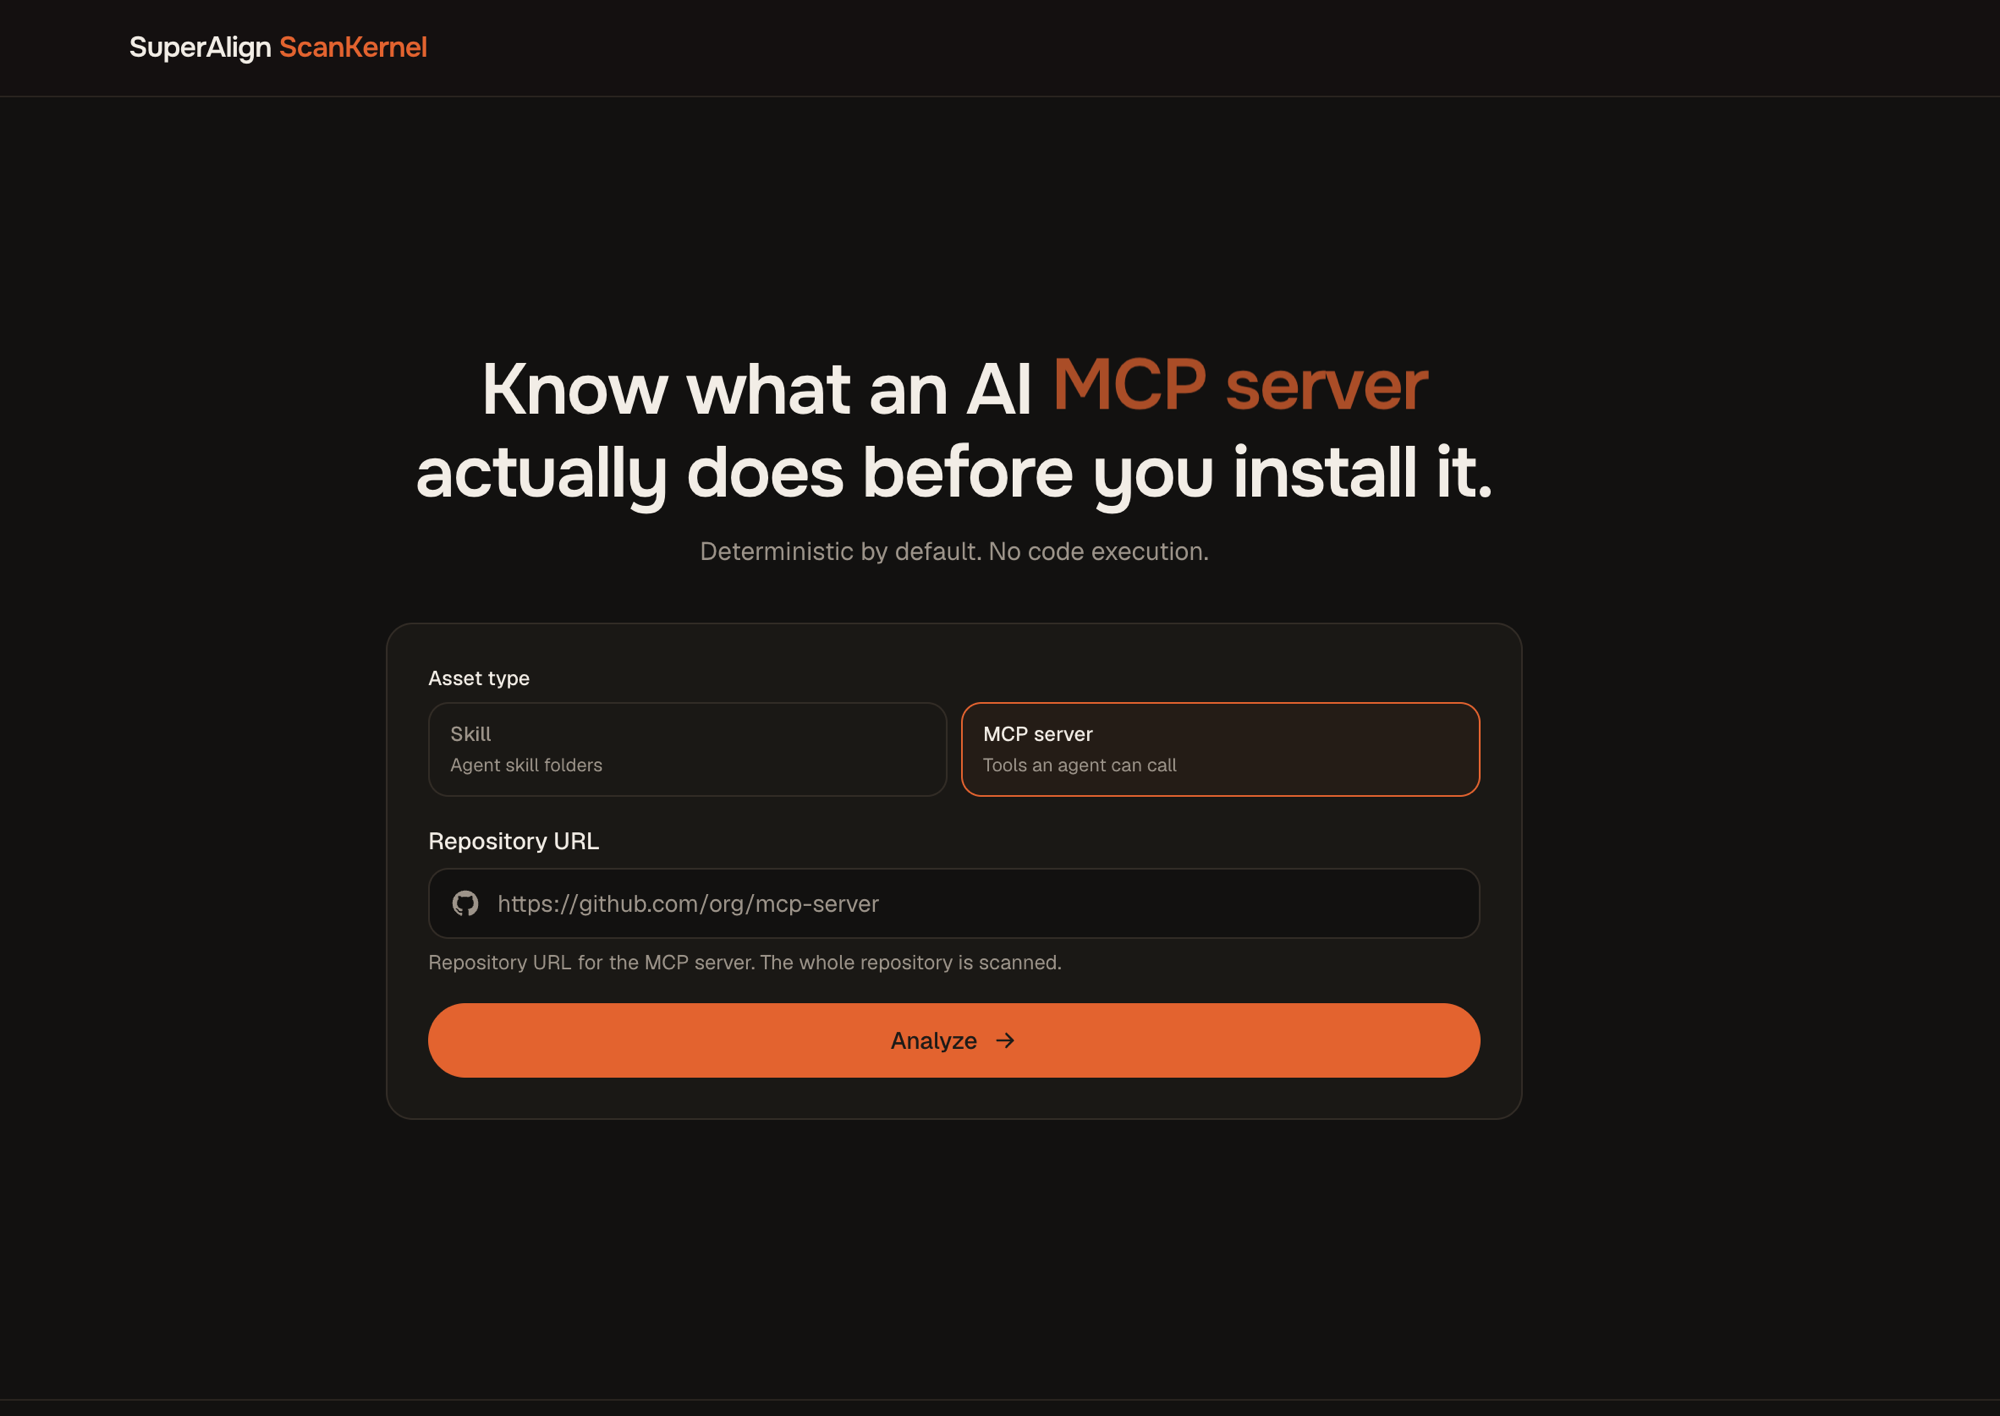
AIRiskDB now scans Model Context Protocol (MCP) servers alongside agent skills. Switch the asset type selector to MCP server, paste any GitHub repository URL, and get an instant security read on the tools and capabilities you are about to connect to your agents — before granting them access to your environment.
15 MCP security checks. Built specifically for the MCP architecture, detections cover command injection, server-side request forgery (SSRF), path traversal, data exfiltration, authorization bypass, prompt injection, and supply chain risks. Every finding lands with a severity, the exact file and line, and an actionable explanation.
Know what each tool can do. Scan results profile the full attack surface of the server: counting registered tools, resources, and prompts, while breaking down permissions. You can clearly see whether a tool is read-only or has high-impact capabilities like executing shell commands, mutating files, or calling external APIs.
Evidence in context. Finding details now include source code snippets so you can review the problematic code directly in the dashboard. Missing lockfile warnings point straight to the package manifest (such as pyproject.toml or package.json), showing you exactly where dependencies need to be pinned.
Faster Python Scans
Simultaneous file scanning. We’ve overhauled Python file analysis to run concurrently across all available CPU cores without blocking. Large repositories with dozens or hundreds of Python files scan smoothly without queue delays, delivering snappy, consistent scan speeds across the board.
Support for modern Python. The code analyzer now natively understands modern Python syntax, including pattern matching (match/case) and walrus operator assignments (:=). Your scans get deeper, uninterrupted behavioral analysis across newer codebases without missing data flows.